



 Chat with AI
Exam 7: Controlling Information Systems: Introduction to Enterprise Risk Management and Internal Control

Exam 1: Introduction to Accounting Information Systems122 Questions
Exam 2: Enterprise Systems141 Questions
Exam 3: Electronic Business E-Business-Systems121 Questions
Exam 4: Documenting Information Systems124 Questions
Exam 5: Database Management Systems175 Questions
Exam 6: Relational Databases and SQL102 Questions
Exam 7: Controlling Information Systems: Introduction to Enterprise Risk Management and Internal Control159 Questions
Exam 8: Controlling Information Systems: Introduction to Pervasive Controls159 Questions
Exam 9: Controlling Information Systems: Business Process and Application Controls134 Questions
Exam 10: The Order Entrysales Oesprocess133 Questions
Exam 11: The Billingaccounts Receivablecash Receipts Barcrprocess134 Questions
Exam 12: The Purchasing Process140 Questions
Exam 13: The Accounts Payablecash Disbursements Apcdprocess118 Questions
Exam 14: The Human Resources Process Hrmanagement and Payroll Processes121 Questions
Exam 15: Integrated Production Processes IPP118 Questions
Exam 16: The General Ledger and Business Reporting Glbrprocess106 Questions
Exam 17: Acquiring and Implementing Accounting Information Systems206 Questions
Select questions type


A(n)______________________________ is program code that can attach itself to other programs or macros thereby infecting those programs and macros.
(Essay)
4.8/5  (86)
(86) The ______________________________ states that "a fundamental aspect of management's stewardship responsibility is to provide shareholders with reasonable assurance that the business is adequately controlled."
(Essay)
4.9/5 (85)
(85) A computer abuse technique called a ____ involves a virus that replicates itself on disks,in memory,or across networks.
(Multiple Choice)
4.7/5 (77)
(77) According to the 2012 Report to the Nation on Occupational Fraud and Abuse,frauds are more likely to be detected by audits or internal controls than through tips.
(True/False)
4.9/5 (76)
(76) SAS No.99 emphasizes auditors should brainstorm fraud risks,increase professional skepticism,use unpredictable audit test patterns,and detect management override of internal controls.
(True/False)
4.9/5 (85)
(85) ____ are the policies and procedures that help ensure that the risk responses are effectively carried out.
(Multiple Choice)
4.8/5 (84)
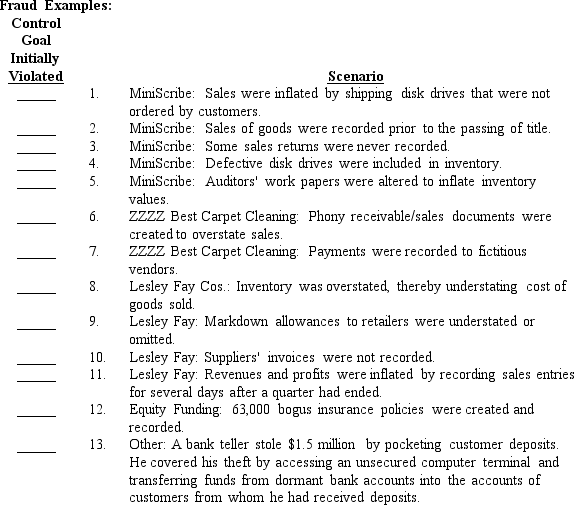
(84) Listed below are 13 specific fraud examples taken from some well-known fraud cases: MiniScribe,ZZZZ Best Carpet Cleaning,Lesley Fay,and Equity Funding.
Required:
For each fraud example,enter a letter corresponding to which information control goal was initially violated-Validity,Completeness,or Accuracy.Some examples might involve more than one violation.
NOTE: When we say initially,we mean what control goal failure led to this example,not what is the present condition.For example,master data might contain information that is inaccurate,but it might have been an inaccurate input that initially caused the data to be inaccurate.
(Essay)
4.8/5 (74)
(74) Management selects risk ________________________- avoiding,accepting,reducing or sharing risk - developing a set of actions to align risks with the entity's risk tolerances and risk appetite.
(Essay)
4.8/5 (85)
(85) The control goal that seeks to protect an organization's resources from loss,destruction,disclosure,copying,sale,or other misuse of an organization's resources is called ensure ______________________________.
(Essay)
4.8/5 (65)
(65) The ERM framework addresses four categories of management objectives.Which category of concerns laws and regulations?
(Multiple Choice)
4.8/5 (62)
(62) Achieving which control goal requires that all valid objects or events are captured and entered into a system's database once and only once?
(Multiple Choice)
4.8/5 (76)
(76) Monitoring is a process that assesses the quality of internal control performance over time.
(True/False)
4.7/5 (79)
(79) As described in COSO,elements of a control environment might include the following:
(Multiple Choice)
4.8/5 (85)
(85) The section of Sarbanes Oxley that requires a company's CEO and CFO to certify quarterly and annual reports is ______________________________.
(Essay)
5.0/5 (93)
(93) The control goal of ensure ______________________________ provides assurance that all valid objects or events which were entered into the computer are in turn reflected in their respective master data once and only once.
(Essay)
5.0/5 (90)
(90) Under the Sarbanes Oxley Act of 2002,the section on Corporate Tax Returns conveys a sense of the Senate that the corporate federal income tax returns be signed by the treasurer.
(True/False)
4.9/5 (78)
(78) According to the 2011 PricewaterhouseCoopers (PwC)Global Economic Crime Survey:
(Multiple Choice)
4.8/5 (77)
(77) Expected gross risk is a function of the initial expected gross risk,reduced risk exposure due to controls,and cost of controls.
(True/False)
4.9/5 (78)
(78) A(n)______________________________ relates to a specific AIS process,such as billing or cash receipts.
(Essay)
4.7/5 (70)
(70) 
Filters
- Essay(0)
- Multiple Choice(0)
- Short Answer(0)
- True False(0)
- Matching(0)