



 Chat with AI
Exam 16: CompTIA Security+ 2021

Exam 1: CompTIA A+ Certification Exam: Core 1471 Questions
Exam 2: CompTIA A+ Certification Exam: Core 2409 Questions
Exam 3: CompTIA Advanced Security Practitioner (CASP+) CAS-003442 Questions
Exam 4: CompTIA Advanced Security Practitioner (CASP+) CAS-004107 Questions
Exam 5: CompTIA Cloud Essentials+165 Questions
Exam 6: CompTIA CySA+ Certification Exam (CS0-002)294 Questions
Exam 7: CompTIA Cloud+ (CV0-002)48 Questions
Exam 8: CompTIA Cloud+67 Questions
Exam 9: CompTIA IT Fundamentals387 Questions
Exam 10: CompTIA Network+829 Questions
Exam 11: CompTIA Project+540 Questions
Exam 12: CompTIA PenTest+ Certification Exam165 Questions
Exam 13: CompTIA Server+66 Questions
Exam 14: CompTIA Server+ Certification Exam779 Questions
Exam 15: CompTIA Security+1 k+ Questions
Exam 16: CompTIA Security+ 2021129 Questions
Exam 17: CompTIA CTT+ Essentials378 Questions
Exam 18: CompTIA Linux+252 Questions
Select questions type


A company has limited storage space available and an online presence that cannot be down for more than four hours. Which of the following backup methodologies should the company implement to allow for the FASTEST database restore time in the event of a failure, while being mindful of the limited available storage space?
(Multiple Choice)
4.9/5  (80)
(80) A network administrator needs to build out a new datacenter, with a focus on resiliency and uptime. Which of the following would BEST meet this objective? (Choose two.)
(Multiple Choice)
4.7/5 (70)
(70) A security analyst discovers that a company's username and password database was posted on an Internet forum. The usernames and passwords are stored in plain text. Which of the following would mitigate the damage done by this type of data exfiltration in the future?
(Multiple Choice)
4.8/5 (73)
(73) A network administrator would like to configure a site-to-site VPN utilizing IPsec. The administrator wants the tunnel to be established with data integrity, encryption, authentication, and anti-replay functions. Which of the following should the administrator use when configuring the VPN?
(Multiple Choice)
4.8/5 (72)
(72) Which of the following BEST explains the difference between a data owner and a data custodian?
(Multiple Choice)
4.9/5 (76)
(76) A small company that does not have security staff wants to improve its security posture. Which of the following would BEST assist the company?
(Multiple Choice)
4.8/5 (77)
(77) An organization has a growing workforce that is mostly driven by additions to the sales department. Each newly hired salesperson relies on a mobile device to conduct business. The Chief Information Officer (CIO) is wondering if the organization may need to scale down just as quickly as it scaled up. The CIO is also concerned about the organization's security and customer privacy. Which of the following would be BEST to address the CIO's concerns?
(Multiple Choice)
4.9/5 (81)
(81) A user contacts the help desk to report the following: Two days ago, a pop-up browser window prompted the user for a name and password after connecting to the corporate wireless SSID. This had never happened before, but the user entered the information as requested. The user was able to access the Internet but had trouble accessing the department share until the next day. The user is now getting notifications from the bank about unauthorized transactions. Which of the following attack vectors was MOST likely used in this scenario?
(Multiple Choice)
4.9/5 (72)
(72) A security analyst is running a vulnerability scan to check for missing patches during a suspected security incident. During which of the following phases of the response process is this activity MOST likely occurring?
(Multiple Choice)
4.8/5 (87)
(87) Which of the following refers to applications and systems that are used within an organization without consent or approval?
(Multiple Choice)
4.8/5 (78)
(78) A website developer is working on a new e-commerce website and has asked an information security expert for the most appropriate way to store credit card numbers to create an easy reordering process. Which of the following methods would BEST accomplish this goal?
(Multiple Choice)
4.8/5 (84)
(84) A startup company is using multiple SaaS and IaaS platforms to stand up a corporate infrastructure and build out a customer-facing web application. Which of the following solutions would be BEST to provide security, manageability, and visibility into the platforms?
(Multiple Choice)
4.8/5 (64)
(64) A recently discovered zero-day exploit utilizes an unknown vulnerability in the SMB network protocol to rapidly infect computers. Once infected, computers are encrypted and held for ransom. Which of the following would BEST prevent this attack from reoccurring?
(Multiple Choice)
4.8/5 (81)
(81) A user recently entered a username and password into a recruiting application website that had been forged to look like the legitimate site. Upon investigation, a security analyst identifies the following: The legitimate website's IP address is 10.1.1.20 and eRecruit.local resolves to this IP. The forged website's IP address appears to be 10.2.12.99, based on NetFlow records. All three of the organization's DNS servers show the website correctly resolves to the legitimate IP. DNS query logs show one of the three DNS servers returned a result of 10.2.12.99 (cached) at the approximate time of the suspected compromise. Which of the following MOST likely occurred?
(Multiple Choice)
4.9/5 (88)
(88) A company recently experienced a data breach and the source was determined to be an executive who was charging a phone in a public area. Which of the following would MOST likely have prevented this breach?
(Multiple Choice)
4.9/5 (79)
(79) A company processes highly sensitive data and senior management wants to protect the sensitive data by utilizing classification labels. Which of the following access control schemes would be BEST for the company to implement?
(Multiple Choice)
4.9/5 (79)
(79) A user reports constant lag and performance issues with the wireless network when working at a local coffee shop. A security analyst walks the user through an installation of Wireshark and gets a five-minute pcap to analyze. The analyst observes the following output: 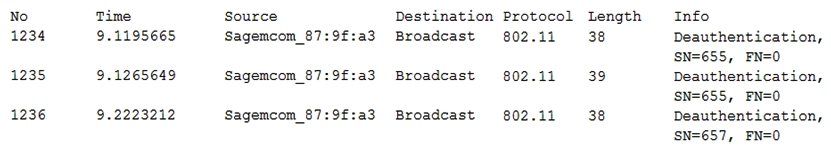 Which of the following attacks does the analyst MOST likely see in this packet capture?
 (Multiple Choice)
4.8/5 (61)
(61) A cybersecurity administrator has a reduced team and needs to operate an on-premises network and security infrastructure efficiently. To help with the situation, the administrator decides to hire a service provider. Which of the following should the administrator use?
(Multiple Choice)
4.9/5 (92)
(92) Which of the following is a team of people dedicated to testing the effectiveness of organizational security programs by emulating the techniques of potential attackers?
(Multiple Choice)
4.8/5 (77)
(77) A cybersecurity analyst reviews the log files from a web server and sees a series of files that indicate a directory-traversal attack has occurred. Which of the following is the analyst MOST likely seeing?
(Multiple Choice)
4.8/5 (93)
(93) 
Filters
- Essay(0)
- Multiple Choice(0)
- Short Answer(0)
- True False(0)
- Matching(0)