



 Chat with AI
Exam 16: CompTIA Security+ 2021

Exam 1: CompTIA A+ Certification Exam: Core 1471 Questions
Exam 2: CompTIA A+ Certification Exam: Core 2409 Questions
Exam 3: CompTIA Advanced Security Practitioner (CASP+) CAS-003442 Questions
Exam 4: CompTIA Advanced Security Practitioner (CASP+) CAS-004107 Questions
Exam 5: CompTIA Cloud Essentials+165 Questions
Exam 6: CompTIA CySA+ Certification Exam (CS0-002)294 Questions
Exam 7: CompTIA Cloud+ (CV0-002)48 Questions
Exam 8: CompTIA Cloud+67 Questions
Exam 9: CompTIA IT Fundamentals387 Questions
Exam 10: CompTIA Network+829 Questions
Exam 11: CompTIA Project+540 Questions
Exam 12: CompTIA PenTest+ Certification Exam165 Questions
Exam 13: CompTIA Server+66 Questions
Exam 14: CompTIA Server+ Certification Exam779 Questions
Exam 15: CompTIA Security+1 k+ Questions
Exam 16: CompTIA Security+ 2021129 Questions
Exam 17: CompTIA CTT+ Essentials378 Questions
Exam 18: CompTIA Linux+252 Questions
Select questions type


An organization wants to implement a third factor to an existing multifactor authentication. The organization already uses a smart card and password. Which of the following would meet the organization's needs for a third factor?
(Multiple Choice)
4.8/5  (90)
(90) During an incident response, a security analyst observes the following log entry on the web server:  Which of the following BEST describes the type of attack the analyst is experiencing?
 (Multiple Choice)
4.8/5 (94)
(94) Which of the following cloud models provides clients with servers, storage, and networks but nothing else?
(Multiple Choice)
4.8/5 (86)
(86) A host was infected with malware. During the incident response, Joe, a user, reported that he did not receive any emails with links, but he had been browsing the Internet all day. Which of the following would MOST likely show where the malware originated?
(Multiple Choice)
4.9/5 (71)
(71) An enterprise has hired an outside security firm to conduct penetration testing on its network and applications. The firm has been given all the developer's documentation about the internal architecture. Which of the following BEST represents the type of testing that will occur?
(Multiple Choice)
4.8/5 (83)
(83) A company recently set up an e-commerce portal to sell its product online. The company wants to start accepting credit cards for payment, which requires compliance with a security standard. Which of the following standards must the company comply with before accepting credit cards on its e-commerce platform?
(Multiple Choice)
4.8/5 (66)
(66) To secure an application after a large data breach, an e-commerce site will be resetting all users' credentials. Which of the following will BEST ensure the site's users are not compromised after the reset?
(Multiple Choice)
4.8/5 (76)
(76) An organization is concerned that its hosted web servers are not running the most updated version of the software. Which of the following would work BEST to help identify potential vulnerabilities?
(Multiple Choice)
4.9/5 (78)
(78) Which of the following is MOST likely to outline the roles and responsibilities of data controllers and data processors?
(Multiple Choice)
4.8/5 (96)
(96) A researcher has been analyzing large data sets for the last ten months. The researcher works with colleagues from other institutions and typically connects via SSH to retrieve additional data. Historically, this setup has worked without issue, but the researcher recently started getting the following message: 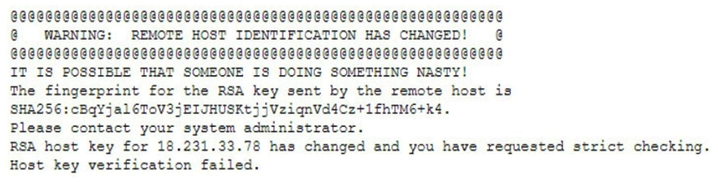 Which of the following network attacks is the researcher MOST likely experiencing?
 (Multiple Choice)
4.7/5 (78)
(78) An organization is developing an authentication service for use at the entry and exit ports of country borders. The service will use data feeds obtained from passport systems, passenger manifests, and high-definition video feeds from CCTV systems that are located at the ports. The service will incorporate machine-learning techniques to eliminate biometric enrollment processes while still allowing authorities to identify passengers with increasing accuracy over time. The more frequently passengers travel, the more accurately the service will identify them. Which of the following biometrics will MOST likely be used, without the need for enrollment? (Choose two.)
(Multiple Choice)
4.9/5 (86)
(86) A smart switch has the ability to monitor electrical levels and shut off power to a building in the event of power surge of power surge or other fault situation. The switch was installed on a wired network in a hospital and is monitored by the facilities department via a cloud application. The security administrator isolated the switch on a separate VLAN and set up a patching routine. Which of the following steps should also be taken to harden the smart switch?
(Multiple Choice)
4.9/5 (75)
(75) A company provides mobile devices to its users to permit access to email and enterprise applications. The company recently started allowing users to select from several different vendors and device models. When configuring the MDM, which of the following is a key security implication of this heterogeneous device approach?
(Multiple Choice)
4.7/5 (67)
(67) A document that appears to be malicious has been discovered in an email that was sent to a company's Chief Financial Officer (CFO). Which of the following would be BEST to allow a security analyst to gather information and confirm it is a malicious document without executing any code it may contain?
(Multiple Choice)
4.8/5 (90)
(90) A retail executive recently accepted a job with a major competitor. The following week, a security analyst reviews the security logs and identifies successful logon attempts to access the departed executive's accounts. Which of the following security practices would have addressed the issue?
(Multiple Choice)
4.8/5 (90)
(90) Users at an organization have been installing programs from the Internet on their workstations without first receiving proper authorization. The organization maintains a portal from which users can install standardized programs. However, some users have administrative access on their workstations to enable legacy programs to function properly. Which of the following should the security administrator consider implementing to address this issue?
(Multiple Choice)
4.7/5 (77)
(77) A security analyst receives a SIEM alert that someone logged in to the appadmin test account, which is only used for the early detection of attacks. The security analyst then reviews the following application log: 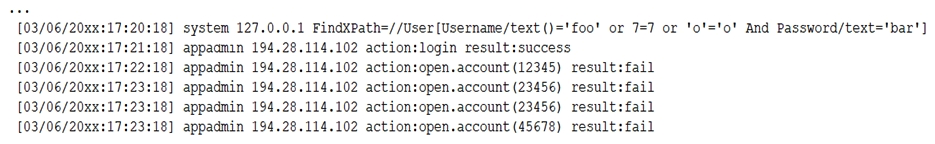 Which of the following can the security analyst conclude?
 (Multiple Choice)
4.8/5 (77)
(77) A security analyst is investigating an incident that was first reported as an issue connecting to network shares and the Internet. While reviewing logs and tool output, the analyst sees the following: 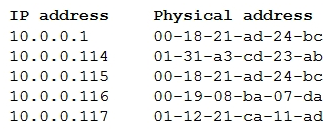 Which of the following attacks has occurred?
 (Multiple Choice)
4.8/5 (81)
(81) An organization has implemented a policy requiring the use of conductive metal lockboxes for personal electronic devices outside of a secure research lab. Which of the following did the organization determine to be the GREATEST risk to intellectual property when creating this policy?
(Multiple Choice)
4.9/5 (82)
(82) A company is designing the layout of a new datacenter so it will have an optimal environmental temperature. Which of the following must be included? (Choose two.)
(Multiple Choice)
4.8/5 (90)
(90) 
Filters
- Essay(0)
- Multiple Choice(0)
- Short Answer(0)
- True False(0)
- Matching(0)