



 Chat with AI
Exam 3: EC-Council Information Security Manager (E|ISM)

Exam 1: EC-Council Certified Incident Handler80 Questions
Exam 2: Certified Network Defender579 Questions
Exam 3: EC-Council Information Security Manager (E|ISM)131 Questions
Exam 4: EC-Council Certified CISO27 Questions
Exam 5: ECCouncil Computer Hacking Forensic Investigator317 Questions
Exam 6: EC-Council Certified Security Analyst24 Questions
Select questions type


Which of the following functions implements and oversees the use of controls to reduce risk when creating an information security program?
(Multiple Choice)
4.9/5  (81)
(81) Before performing a logical or physical search of a drive in Encase, what must be added to the program?
(Multiple Choice)
4.8/5 (76)
(76) You currently cannot provide for 24/7 coverage of your security monitoring and incident response duties and your company is resistant to the idea of adding more full-time employees to the payroll. Which combination of solutions would help to provide the coverage needed without the addition of more dedicated staff? (choose the best answer):
(Multiple Choice)
4.8/5 (69)
(69) While looking through the IIS log file of a web server, you find the following entries: 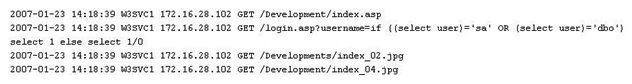 What is evident from this log file?
 (Multiple Choice)
4.7/5 (83)
(83) A severe security threat has been detected on your corporate network. As CISO you quickly assemble key members of the Information Technology team and business operations to determine a modification to security controls in response to the threat. This is an example of:
(Multiple Choice)
4.7/5 (97)
(97) A CISO implements smart cards for credential management, and as a result has reduced costs associated with help desk operations supporting password resets. This demonstrates which of the following principles?
(Multiple Choice)
5.0/5 (91)
(91) When operating under severe budget constraints a CISO will have to be creative to maintain a strong security organization. Which example below is the MOST creative way to maintain a strong security posture during these difficult times?
(Multiple Choice)
4.8/5 (63)
(63) Daryl, a computer forensics investigator, has just arrived at the house of an alleged computer hacker. Daryl takes pictures and tags all computer and peripheral equipment found in the house. Daryl packs all the items found in his van and takes them back to his lab for further examination. At his lab, Michael his assistant helps him with the investigation. Since Michael is still in training, Daryl supervises all of his work very carefully. Michael is not quite sure about the procedures to copy all the data off the computer and peripheral devices. How many data acquisition tools should Michael use when creating copies of the evidence for the investigation?
(Multiple Choice)
4.8/5 (80)
(80) What will the following Linux command accomplish? dd if=/dev/mem of=/home/sam/mem.bin bs=1024
(Multiple Choice)
4.9/5 (75)
(75) You are the CISO of a commercial social media organization. The leadership wants to rapidly create new methods of sharing customer data through creative linkages with mobile devices. You have voiced concern about privacy regulations but the velocity of the business is given priority. Which of the following BEST describes this organization?
(Multiple Choice)
4.9/5 (82)
(82) A picture file is recovered from a computer under investigation. During the investigation process, the file is enlarged 500% to get a better view of its contents. The picture quality is not degraded at all from this process. What kind of picture is this file. What kind of picture is this file?
(Multiple Choice)
4.9/5 (75)
(75) In handling computer-related incidents, which IT role should be responsible for recovery, containment, and prevention to constituents?
(Multiple Choice)
5.0/5 (88)
(88) Risk appetite is typically determined by which of the following organizational functions?
(Multiple Choice)
4.7/5 (83)
(83) Using Linux to carry out a forensics investigation, what would the following command accomplish? dd if=/usr/home/partition.image of=/dev/sdb2 bs=4096 conv=notrunc,noerror
(Multiple Choice)
4.8/5 (71)
(71) How often must a company keep log files for them to be admissible in a court of law?
(Multiple Choice)
5.0/5 (73)
(73) How often should the SSAE16 report of your vendors be reviewed?
(Multiple Choice)
4.9/5 (70)
(70) Which of the following is critical in creating a security program aligned with an organization's goals?
(Multiple Choice)
4.9/5 (63)
(63) A CISO decides to analyze the IT infrastructure to ensure security solutions adhere to the concepts of how hardware and software is implemented and managed within the organization. Which of the following principles does this best demonstrate?
(Multiple Choice)
4.9/5 (75)
(75) Which of the following methodologies references the recommended industry standard that Information security project managers should follow?
(Multiple Choice)
4.9/5 (87)
(87) 
Filters
- Essay(0)
- Multiple Choice(0)
- Short Answer(0)
- True False(0)
- Matching(0)