



 Chat with AI
Exam 12: CompTIA PenTest+ Certification Exam

Exam 1: CompTIA A+ Certification Exam: Core 1471 Questions
Exam 2: CompTIA A+ Certification Exam: Core 2409 Questions
Exam 3: CompTIA Advanced Security Practitioner (CASP+) CAS-003442 Questions
Exam 4: CompTIA Advanced Security Practitioner (CASP+) CAS-004107 Questions
Exam 5: CompTIA Cloud Essentials+165 Questions
Exam 6: CompTIA CySA+ Certification Exam (CS0-002)294 Questions
Exam 7: CompTIA Cloud+ (CV0-002)48 Questions
Exam 8: CompTIA Cloud+67 Questions
Exam 9: CompTIA IT Fundamentals387 Questions
Exam 10: CompTIA Network+829 Questions
Exam 11: CompTIA Project+540 Questions
Exam 12: CompTIA PenTest+ Certification Exam165 Questions
Exam 13: CompTIA Server+66 Questions
Exam 14: CompTIA Server+ Certification Exam779 Questions
Exam 15: CompTIA Security+1 k+ Questions
Exam 16: CompTIA Security+ 2021129 Questions
Exam 17: CompTIA CTT+ Essentials378 Questions
Exam 18: CompTIA Linux+252 Questions
Select questions type


A security consultant is trying to attack a device with a previously identified user account. 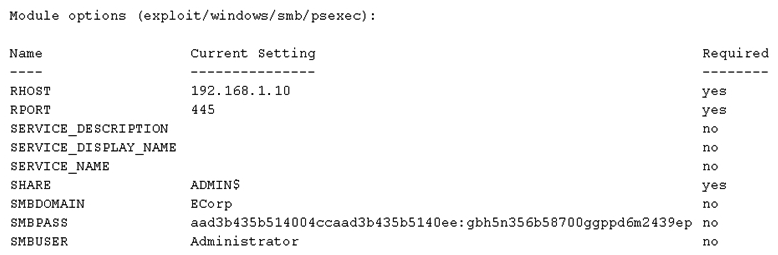 Which of the following types of attacks is being executed?
 (Multiple Choice)
4.8/5  (83)
(83) A penetration tester has compromised a host. Which of the following would be the correct syntax to create a Netcat listener on the device?
(Multiple Choice)
4.9/5 (81)
(81) A penetration tester has run multiple vulnerability scans against a target system. Which of the following would be unique to a credentialed scan?
(Multiple Choice)
4.9/5 (85)
(85) Which of the following excerpts would come from a corporate policy?
(Multiple Choice)
5.0/5 (94)
(94) A tester has captured a NetNTLMv2 hash using Responder. Which of the following commands will allow the tester to crack the hash using a mask attack?
(Multiple Choice)
4.8/5 (83)
(83) A penetration tester is planning to conduct a distributed dictionary attack on a government domain against the login portal. The tester will leverage multiple proxies to mask the origin IPs of the attack. Which of the following threat actors will be emulated?
(Multiple Choice)
4.8/5 (86)
(86) A penetration tester is in the process of writing a report that outlines the overall level of risk to operations. In which of the following areas of the report should the penetration tester put this?
(Multiple Choice)
4.9/5 (86)
(86) A healthcare organization must abide by local regulations to protect and attest to the protection of personal health information of covered individuals. Which of the following conditions should a penetration tester specifically test for when performing an assessment? (Select TWO).
(Multiple Choice)
4.9/5 (61)
(61) Which of the following is the reason why a penetration tester would run the chkconfig --del servicename command at the end of an engagement?
(Multiple Choice)
4.8/5 (80)
(80) A penetration tester is testing a web application and is logged in as a lower-privileged user. The tester runs arbitrary JavaScript within an application, which sends an XMLHttpRequest, resulting in exploiting features to which only an administrator should have access. Which of the following controls would BEST mitigate the vulnerability?
(Multiple Choice)
4.9/5 (98)
(98) A penetration tester is reviewing the following output from a wireless sniffer: 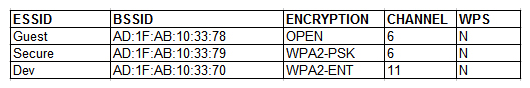 Which of the following can be extrapolated from the above information?
 (Multiple Choice)
4.8/5 (87)
(87) For which of the following reasons does a penetration tester need to have a customer's point-of-contact information available at all times? (Choose three.)
(Multiple Choice)
4.9/5 (79)
(79) Black box penetration testing strategy provides the tester with:
(Multiple Choice)
4.8/5 (85)
(85) A penetration tester is checking a script to determine why some basic math errors are persisting. The expected result was the program outputting "True". 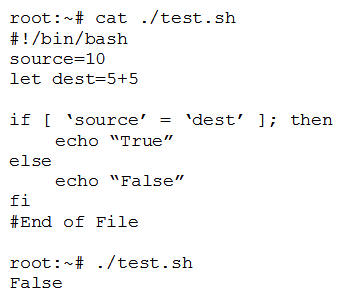 Given the output from the console above, which of the following explains how to correct the errors in the script? (Choose two.)
 (Multiple Choice)
4.7/5 (69)
(69) Click the exhibit button. 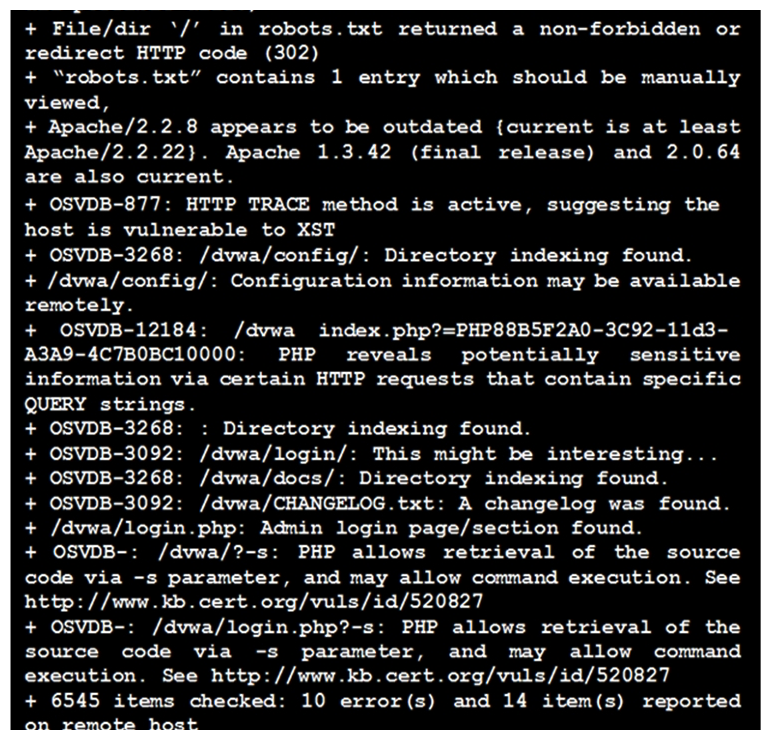 Given the Nikto vulnerability, scan output shown in the exhibit, which of the following exploitation techniques might be used to exploit the target system? (Choose two.)
 (Multiple Choice)
4.7/5 (84)
(84) A penetration tester is able to move laterally throughout a domain with minimal roadblocks after compromising a single workstation. Which of the following mitigation strategies would be BEST to recommend in the report? (Select THREE).
(Multiple Choice)
4.8/5 (67)
(67) If a security consultant comes across a password hash that resembles the following: b117525b345470c29ca3d8ae0b556ba8 Which of the following formats is the correct hash type?
(Multiple Choice)
4.8/5 (78)
(78) While performing privilege escalation on a Windows 7 workstation, a penetration tester identifies a service that imports a DLL by name rather than an absolute path. To exploit this vulnerability, which of the following criteria must be met?
(Multiple Choice)
4.8/5 (80)
(80) A penetration test was performed by an on-staff junior technician. During the test, the technician discovered the web application could disclose an SQL table with user account and password information. Which of the following is the MOST effective way to notify management of this finding and its importance?
(Multiple Choice)
4.7/5 (79)
(79) Which of the following actions BEST matches a script kiddie's threat actor?
(Multiple Choice)
4.9/5 (73)
(73) 
Filters
- Essay(0)
- Multiple Choice(0)
- Short Answer(0)
- True False(0)
- Matching(0)