



 Chat with AI
Exam 4: CIW v5 Security Essentials

Exam 1: CIW v5 Site Designer83 Questions
Exam 2: CIW E-Commerce Designer86 Questions
Exam 3: CIW v5 Database Design Specialist75 Questions
Exam 4: CIW v5 Security Essentials48 Questions
Exam 5: CIW Web Foundations Associate138 Questions
Exam 6: CIW Internet Business Associate14 Questions
Exam 7: CIW Site Development Associate15 Questions
Exam 8: CIW Network Technology Associate8 Questions
Exam 9: CIW User Interface Designer49 Questions
Exam 10: CIW JavaScript Specialist30 Questions
Select questions type


You have determined that the company Web server has several vulnerabilities, including a buffer overflow that has resulted in an attack. The Web server uses PHP and has direct connections to an Oracle database server. It also uses many CGI scripts. Which of the following is the most effective way to respond to this attack?
(Multiple Choice)
4.9/5  (86)
(86) You have implemented a service on a Linux system that allows a user to read and edit resources. What is the function of this service?
(Multiple Choice)
4.8/5 (84)
(84) Consider the following diagram: 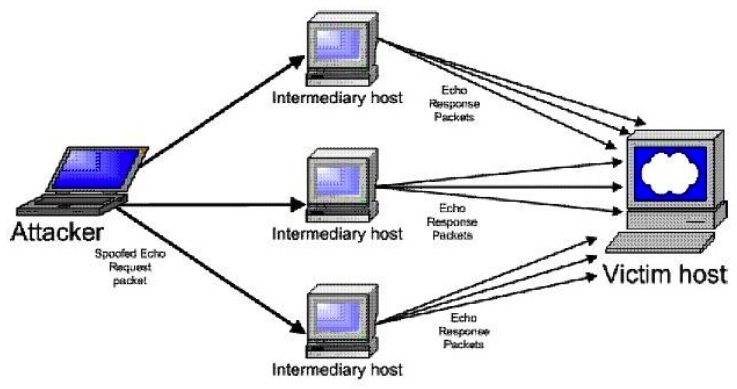 Which type of attack is occurring?
 (Multiple Choice)
4.8/5 (74)
(74) You want to create a quick solution that allows you to obtain real-time login information for the administrative account on an LDAP server that you feel may become a target. Which of the following will accomplish this goal?
(Multiple Choice)
4.9/5 (71)
(71) A security breach has occurred involving the company e-commerce server. Customer credit card data has been released to unauthorized third parties. Which of the following lists the appropriate parties to inform?
(Multiple Choice)
4.8/5 (83)
(83) A new video conferencing device has been installed on the network. You have been assigned to troubleshoot a connectivity problem between remote workers and the central company. Specifically, remote workers are having problems making any connection at all. Which technique will most likely help you solve this problem while retaining the existing level of security at the firewall?
(Multiple Choice)
4.8/5 (84)
(84) A security breach has occurred in which a third party was able to obtain and misuse legitimate authentication information. After investigation, you determined that the specific cause for the breach was that end users have been placing their passwords underneath their keyboards. Which step will best help you resolve this problem?
(Multiple Choice)
4.8/5 (85)
(85) 
Filters
- Essay(0)
- Multiple Choice(0)
- Short Answer(0)
- True False(0)
- Matching(0)