Multiple Choice
A security administrator is implementing a new WAF solution and has placed some of the web servers behind the WAF, with the WAF set to audit mode. When reviewing the audit logs of external requests and posts to the web servers, the administrator finds the following entry: 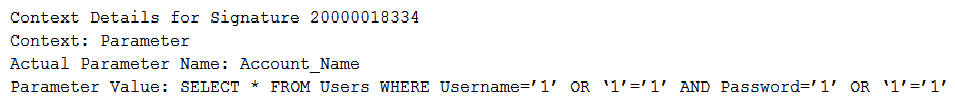 Based on this data, which of the following actions should the administrator take?
A) Alert the web server administrators to a misconfiguration.
B) Create a blocking policy based on the parameter values.
C) Change the parameter name 'Account_Name' identified in the log. Change the parameter name 'Account_Name' identified in the log.
D) Create an alert to generate emails for abnormally high activity.
Correct Answer:

Verified
Correct Answer:
Verified
Q503: A cybersecurity analyst needs to implement secure
Q504: Two companies are enabling TLS on their
Q505: An application team is performing a load-balancing
Q506: Which of the following is a technical
Q507: A systems administrator is configuring a system
Q509: A penetration tester harvests potential usernames from
Q510: Which of the following metrics are used
Q511: Which of the following implements two-factor authentication?<br>A)
Q512: Which of the following terms BEST describes
Q513: A mobile device user is concerned about