Multiple Choice
A company's Security Engineer is copying all application logs to centralized Amazon S3 buckets. Currently, each of the company's application is in its own AWS account, and logs are pushed into S3 buckets associated with each account. The Engineer will deploy an AWS Lambda function into each account that copies the relevant log files to the centralized S3 bucket. The Security Engineer is unable to access the log files in the centralized S3 bucket. The Engineer's IAM user policy from the centralized account looks like this: 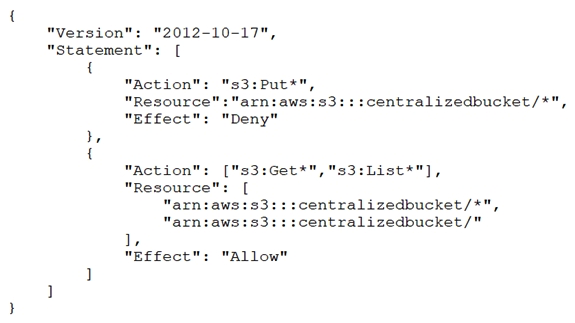 The centralized S3 bucket policy looks like this:
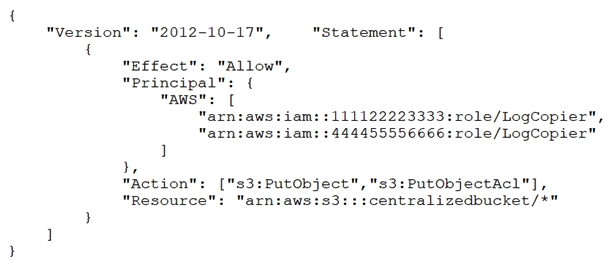 Why is the Security Engineer unable to access the log files?
A) The S3 bucket policy does not explicitly allow the Security Engineer access to the objects in the bucket.
B) The object ACLs are not being updated to allow the users within the centralized account to access the objects.
C) The Security Engineer's IAM policy does not grant permissions to read objects in the S3 bucket.
D) The s3:PutObject and s3:PutObjectAcl permissions should be applied at the S3 bucket level.
Correct Answer:

Verified
Correct Answer:
Verified
Q259: A Systems Engineer has been tasked with
Q260: A security engineer is setting up a
Q261: A company recently experienced a DDoS attack
Q262: A Security Architect is evaluating managed solutions
Q263: An organization has a system in AWS
Q265: Users report intermittent availability of a web
Q266: Which approach will generate automated security alerts
Q267: A company has a VPC with an
Q268: A company maintains sensitive data in an
Q269: While securing the connection between a company's