Multiple Choice
A security administrator notices that the log file of the company`s webserver contains suspicious entries: 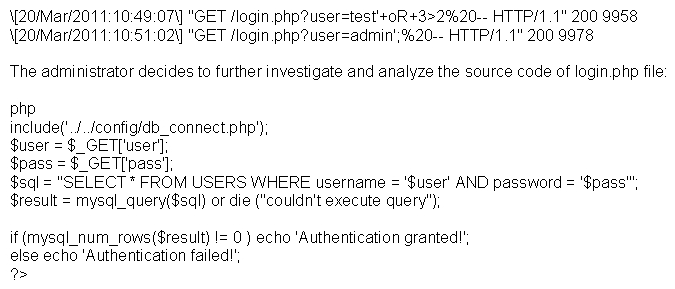 Based on source code analysis, the analyst concludes that the login.php script is vulnerable to
A) command injection.
B) SQL injection.
C) directory traversal.
D) LDAP injection.
Correct Answer:

Verified
Correct Answer:
Verified
Q51: Smart cards use which protocol to transfer
Q52: Which of the following is a hashing
Q53: Some passwords are stored using specialized encryption
Q54: A botnet can be managed through which
Q55: Peter is working on a pen testing
Q57: Martin works as a professional Ethical Hacker
Q58: Which of the following is a primary
Q59: An employee is trying to access the
Q60: What is a successful method for protecting
Q61: What is the process of logging, recording,